 Hassan Maishera
TL;DR
-
Vitalik Buterin says the crypto industry should take threats from AI-accelerated mathematics seriously.
-
He cautions holders against rushing wallet migrations, warning that mistakes can cause funds to be lost.
-
Ethereum researcher Justin Drake has urged preparations for a possible cryptographic emergency he calls “bunker mode.”
-
Buterin identifies lattice-based cryptography as another potential area of risk and favors hash-based constructions where feasible.
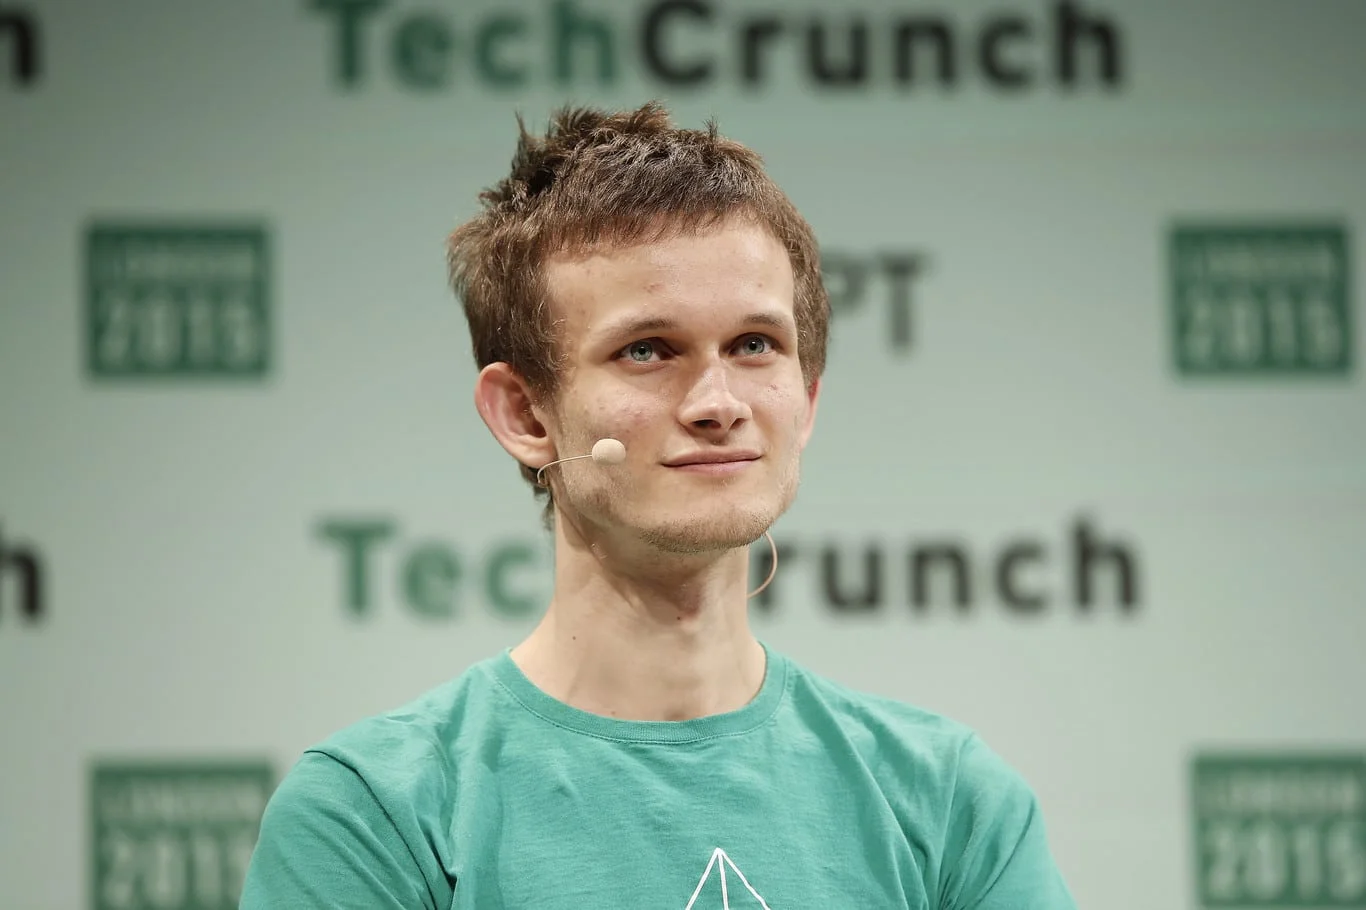
Ethereum co-founder Vitalik Buterin has warned that advances in AI-assisted mathematics could challenge assumptions underlying cryptocurrency security, while urging holders to avoid hurried changes to their wallets.
In a Wednesday post on X, Buterin said keeping assets in addresses that have never signed a transaction can be a reasonable precaution when the move is straightforward. However, he said he does not recommend scrambling to transfer funds.
I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography. The core new area of risk from this viewpoint is, unfortunately, ML-DSA / FHE / lattices. (and it's also another reason, along with quantum, why ECDSA might fall even faster than expected, hence the "fresh address" recommendation) So far most people have been in the mode of thinking "elliptic curves broken, hashes safe, lattices safe". But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math. The basic threat model is: factoring is something that naively takes 2^(n/2) time, but over decades smart people have found and optimized number field sieves, and degraded that to 2^O(n^(1/3)), which is why RSA keys and signatures need to be ~400 bytes (and not 64 bytes). What if there are skeletons in the closet like that, both for elliptic curves and lattices, that we are simply not smart enough to discover - but bots soon will be? This is a major part of the reason why for the past year ethereum's lean roadmap has been going in the "hash-only" direction: no lattices, no ML-DSA, no Falcon, no lattice-based commitments inside ZK proofs, etc. Signatures in lean ethereum are all hash-based, either WOTS or SPHINCS-. For signatures and proofs, we already know how to go hash-only. The bigger challenge is for *public-key encryption* - and this goes far beyond blockchains. Secure communication, anonymizing protocols, lots of things need public-key encryption. And unfortunately there are long-standing mathematical theorems showing why public-key encryption cannot be done with hashes alone. You have to have some kind of trapdoor object that has at least one form of usable "structure" - either group theory (incl. isogenies) or lattices or code-based or potentially in the future even more newfangled and spooky things (local mixing?). But for anything that has structure, you should assume that AI will make at least some progress in breaking that structure. Here, one reasonable inference is that if you want to make something plausibly long-term secure, multiply the key sizes by 10. To me that's a very plausible world and something not at all extreme to predict. If AI will bring us 50 years of math in 2 years, then that 50 years of math may very plausibly include a "naive factoring -> GNFS" level of improvement to our ability to break lattices. In that world, lattices will still exist, but they will have to be significantly bigger to guarantee the same level of safety. And at those new larger sizes, hash-based constructions will beat lattice-based constructions on concrete efficiency in every use case where hash-based constructions are possible at all. Theoretically, of course it's possible that hashes are broken too (eg. P = NP would imply that). But I think P = NP is very unlikely. And intuitively, it's much more likely that a mathematical object has exactly no exploitable structure (like hashes are intended to), than that a mathematical object has exactly ~3 forms of exploitable structure (for elliptic curves: associativity, Schoof, pairings) and not some secret fourth form of structure we have not yet discovered that greatly degrades its security (for elliptic curves, ECDLP and pairing security). Similar for LWE, SVP, RLWE and the zoo of lattice problems. For this reason, we do not yet see any reason to worry and start padding the byte size of hashes (if we start to worry more, we would pad the round count first before doing anything to the byte size). Concrete TLDR, my own personal views: * Hash-based > lattice-based, in those situations where hash-based is possible at all * For anything lattice-based, be much more paranoid on param sizes. Remember that blockchains are only a small portion of the cryptography story; this point goes far beyond blockchains and applies to eg. access to websites, secure messaging, Tor / VPNs ... * For privacy protocols, strongly favor NOT putting encrypted notes onchain. Instead, send them offchain through some third-party mechanism. * If it's not difficult for you, keeping your funds in addresses which have not yet been used to make a transaction is a good idea. If it's easy for you, do it. **But be careful about migrations; I personally have lost more money in botched migrations than I have lost in all hacks combined**. * For multisig wallets, doing confirmations offchain is better than onchain, because this way the signatures of signer wallets do not get exposed to the public, so if ECDSA falls to AI much faster than expected, at least the multisig "gracefully degrades" to a 1-of-1 where the 1 is whoever was gathering the signatures - a much better place to be than "anyone can take the money" https://t.co/oVjwZog2lL
— vitalik.eth (@VitalikButerin) October 7, 2026
He noted that migration mistakes have personally cost him more than hacks, emphasizing the practical risks of acting too quickly.
Justin Drake Calls for Cryptographic Contingency Planning
Buterin’s comments followed a warning from Ethereum Foundation researcher Justin Drake, who urged the industry to prepare for what he described as “bunker mode.”
Drake said the Elliptic Curve Digital Signature Algorithm, or ECDSA, could potentially be broken before sufficiently powerful quantum computers threaten widely used public-key cryptography.
In his worst-case scenario, a breakthrough could arrive within months rather than years. That timeline represents a risk assessment, not a confirmed prediction.
Drake recommended controlled transfers to fresh addresses that keep public keys hidden, while also advising holders against panic or rushed action.
Buterin’s response placed greater emphasis on weighing any precaution against the possibility of errors during migration.
Buterin identified AI-accelerated mathematics as a reason cryptographic vulnerabilities could emerge sooner than expected.
He said much of the industry’s planning has assumed that elliptic-curve cryptography could fail while hash functions and lattice-based systems remain secure.
However, he believes advances in AI-assisted mathematics could also significantly weaken the concrete security of lattice-based constructions over the next two years.
He named ML-DSA, fully homomorphic encryption, and other lattice schemes among the areas requiring attention. His warning concerns their potential resistance to future attacks, rather than an announcement of a demonstrated compromise.
AI Mathematics Advances Prompt Fresh Security Questions
The discussion followed reports that OpenAI published hundreds of mathematical manuscripts generated by an internal model on Tuesday.
Drake characterized the development as a sign of rapidly advancing mathematical AI capabilities.
The researchers’ concern is that stronger mathematical tools could uncover weaknesses or improve attacks against cryptographic systems. The reported manuscripts alone do not establish that ECDSA or lattice-based cryptography has been broken.
Buterin said the industry should adopt more conservative lattice parameters and prefer hash-based constructions where practical.
For privacy protocols, he also recommended avoiding the permanent publication of encrypted notes onchain, favoring offchain delivery through third-party mechanisms.
Despite his concerns, Buterin reiterated that holders should avoid hasty upgrades or transfers.
A rushed migration can introduce configuration errors and other operational mistakes, potentially causing losses independently of any cryptographic attack.
His position combines longer-term preparation with caution: developers should reassess security assumptions as AI capabilities advance, while users should carefully evaluate changes before moving assets.